Reactive Abuse Infrastructure
- BY
- ROOT TEAM
- PUBLISHED
- SEPTEMBER 2, 2026
- READING TIME
- 8 MIN READ
Almost nothing is actually wrong with the engineers building anti abuse systems. The infrastructure itself is reactive by design, and that design is the root cause. This is the diagnosis, and the one rule that would change where every system begins.
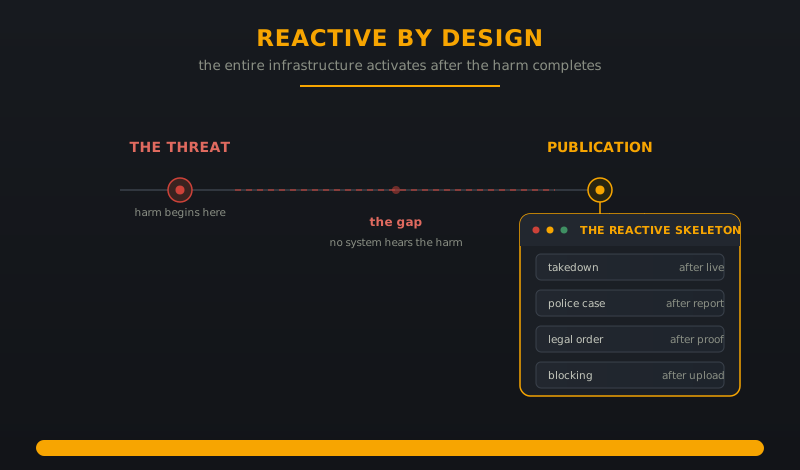
Every anti abuse system in the world shares the same skeleton. A victim reports, but only after content has appeared online. The system responds with takedown requests, platform reports, and sometimes prosecution. The entire machine is built around the instant an image goes public.
We have studied this infrastructure the way we study everything else, by tracing the harm back to its root cause. And the uncomfortable conclusion is that the people building these systems are not the problem. The architecture is. It is reactive by design, and that single design decision is where almost all of the failure lives.
The harm does not begin at publication
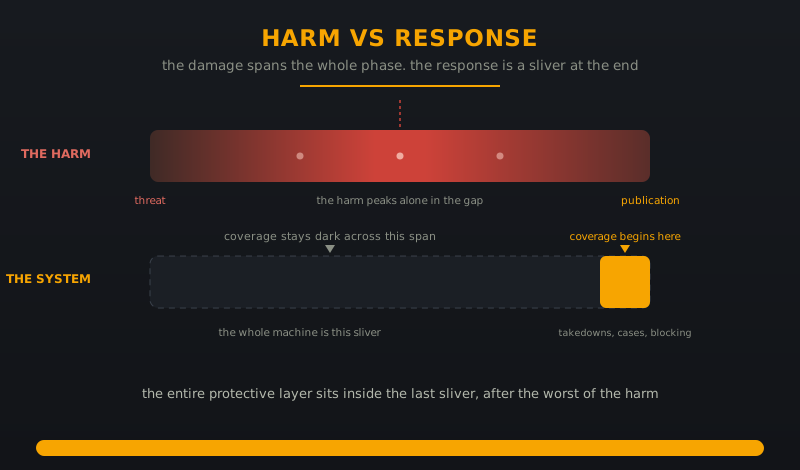
Start with the timeline, because everything follows from it. The worst moment for a victim is not the moment content is published. She never publishes anything. The worst moment is the threat. The moment someone says, "Do what I say, or I publish," she is already experiencing the damage. The coercion. The fear. The extortion. The isolation. These are not warnings that harm is coming. They are the harm itself.
During this phase, no existing system is built to help her. She cannot go to the police, because nothing has been published. She cannot report to a platform, because the content is not public. She cannot get a legal order, because there is no documented abuse in progress. Every institutional pathway requires the harm to have already happened.
In an honour based context, this is not a gap in convenience, it is a gap in survival. The threat to send an image to a family carries the same weight as actually sending it. A woman does not need the image to be public to lose her safety, her autonomy, or her life. But the systems designed to protect her wait for exactly that.
Why the infrastructure cannot see the early phase
The structural reason is that anti abuse infrastructure is built around evidence collection, and evidence collection assumes the misdeed has already occurred. A takedown system needs the content to exist on a platform. Legal proceedings need documented publication. A blocking network needs the image to compute a hash. Every capability is engineered to act on the artifact, never on the moment a person first feels unsafe.
This is not a bug in one product. It is the shared skeleton of the entire industry. Every tool, every hotline, every national scheme is pointed at the same late event, and every one of them is therefore blind to the phase where the most harm actually happens.
That shared design produces a single devastating consequence. To get help, a victim must surrender the one thing she cannot afford to give.
To report, she must share the image. To preserve evidence, she must upload it somewhere. To prove abuse, she must show it to someone. Every path to protection asks her to hand over the material that endangers her, and then to trust that a database full of other people's most private moments will never be the next thing to fail.
So she asks the obvious questions. Who holds this? How is it stored? What happens if you are breached? In a context where exposure can end a life, these are not abstract risks. They are survival calculations. And when the answer is that the system will hold the image being used against her, she makes the only choice that makes sense. She stays silent.
The gap feeds itself
Here is the cruelest loop in the whole architecture. Because victims do not report during the threat phase, institutions collect no data on how common coercion actually is. Without data, there is no mandate to build proactive systems. Without proactive systems, victims keep suffering alone in the gap. The absence of reports is quietly read as the absence of harm, when it is actually the strongest evidence of how broken the door is.
And when publication finally does occur, the report that arrives is already damaged. The evidence is scattered. The timeline is unclear. The victim has endured the worst of it alone and is now being asked to produce a clean record on demand. The investigation starts uphill from the very beginning.
Worse, the institution that collected her private image as evidence is now itself a vulnerability. The material exists. People have access. Systems get breached. The very organization built to protect her becomes another vector for revictimization. The protective infrastructure, by holding the thing that endangers her, quietly becomes part of the threat.
Naming the root cause
So here is the root cause, stated without decoration. Reactive abuse infrastructure is oriented around the wrong event, the artifact, and the wrong object, the image. It activates only after the harm is complete, and it asks the person in danger to hand over the very material that endangers her to receive help. These two design choices reinforce each other, and together they guarantee that the system fails exactly when it matters most.
Once you name it, the fix becomes a rule rather than a wish. A system that closes this gap must activate on the threat, not the publication, and it must refuse to hold the material that endangers the person. Not as a policy promise, but as a technical impossibility.
The threat becomes the entry point. A credible threat report triggers immediate safety guidance and a tamper evident record. A fingerprint is computed on the victim's own device, and only the hash moves on, so platforms can block a match later without the picture ever leaving her phone. The system stores the threat evidence richly, the messages, the sender, the demands, and refuses the photograph entirely. A breach reveals threat correspondence, never the weaponized material, because the material was never there to be taken.
A transparent risk engine surfaces signals for a human reviewer, but never decides alone. A minor forces a safeguarding path. A threat of violence forces human review. High risk cases never proceed on automation, because the illusion of automation is the most dangerous object in any room holding human vulnerability.
What change actually costs
We need to be honest about the price. The software is the easy part. The encrypted vault that refuses images, the tamper evident ledger, the explainable risk engine, these are all buildable and we have built them. What makes this credible and expensive is trained human reviewers, forensic support, institutional partnerships, and sustained trust. A system that acts before publication will generate reports that look like speculation until the threat materializes. It will require human judgment under pressure. It will require legal frameworks that recognize coercion as harm, not just publication.
And it will require measuring success differently. The current system counts complaints filed and takedowns executed. A proactive system must instead be measured by the harm it prevents from ever beginning. That is a harder metric, and it is the only honest one. Fewer cases where publication happened because intervention happened earlier. Faster time from threat to protection. Higher escalation for high risk cases. And zero revictimization caused by the system itself.
The uncomfortable conclusion
The reason reactive abuse infrastructure keeps failing is not a shortage of well meaning engineers or good intentions. It is that the entire architecture is pointed at the wrong moment and the wrong object. It waits for publication, and it demands the image. Both choices are structural, both are universal, and both are fixable the moment you stop confusing the artifact with the harm.
This is a root cause, the way our studio thinks about root causes. The symptom is that victims report too late. The deeper cause is that the infrastructure is designed to only ever see them once it is too late. Fix the trigger and the storage, and you fix the whole machine. Leave them and you are polishing a door that opens after the fire, and asks the person inside to bring the thing that is burning.
Try it this week
Look at whatever safety feature, policy, or reporting flow your own team owns. Ask two questions. At what moment does it first help a person, at the threat or at the artifact? And what does it ask that person to hand over to receive help? If it waits for the artifact and asks for the material that endangers them, you have a reactive abuse infrastructure of your own. Start the safety earlier and hold less. That is the cause. That is where the fix has to begin. Finding the cause is our daily work.